Beyond IP, DNS, and Centralized CAs: Rebuilding Peer-to-Peer Secure Connectivity with DID-TLS and Symmetric Mesh
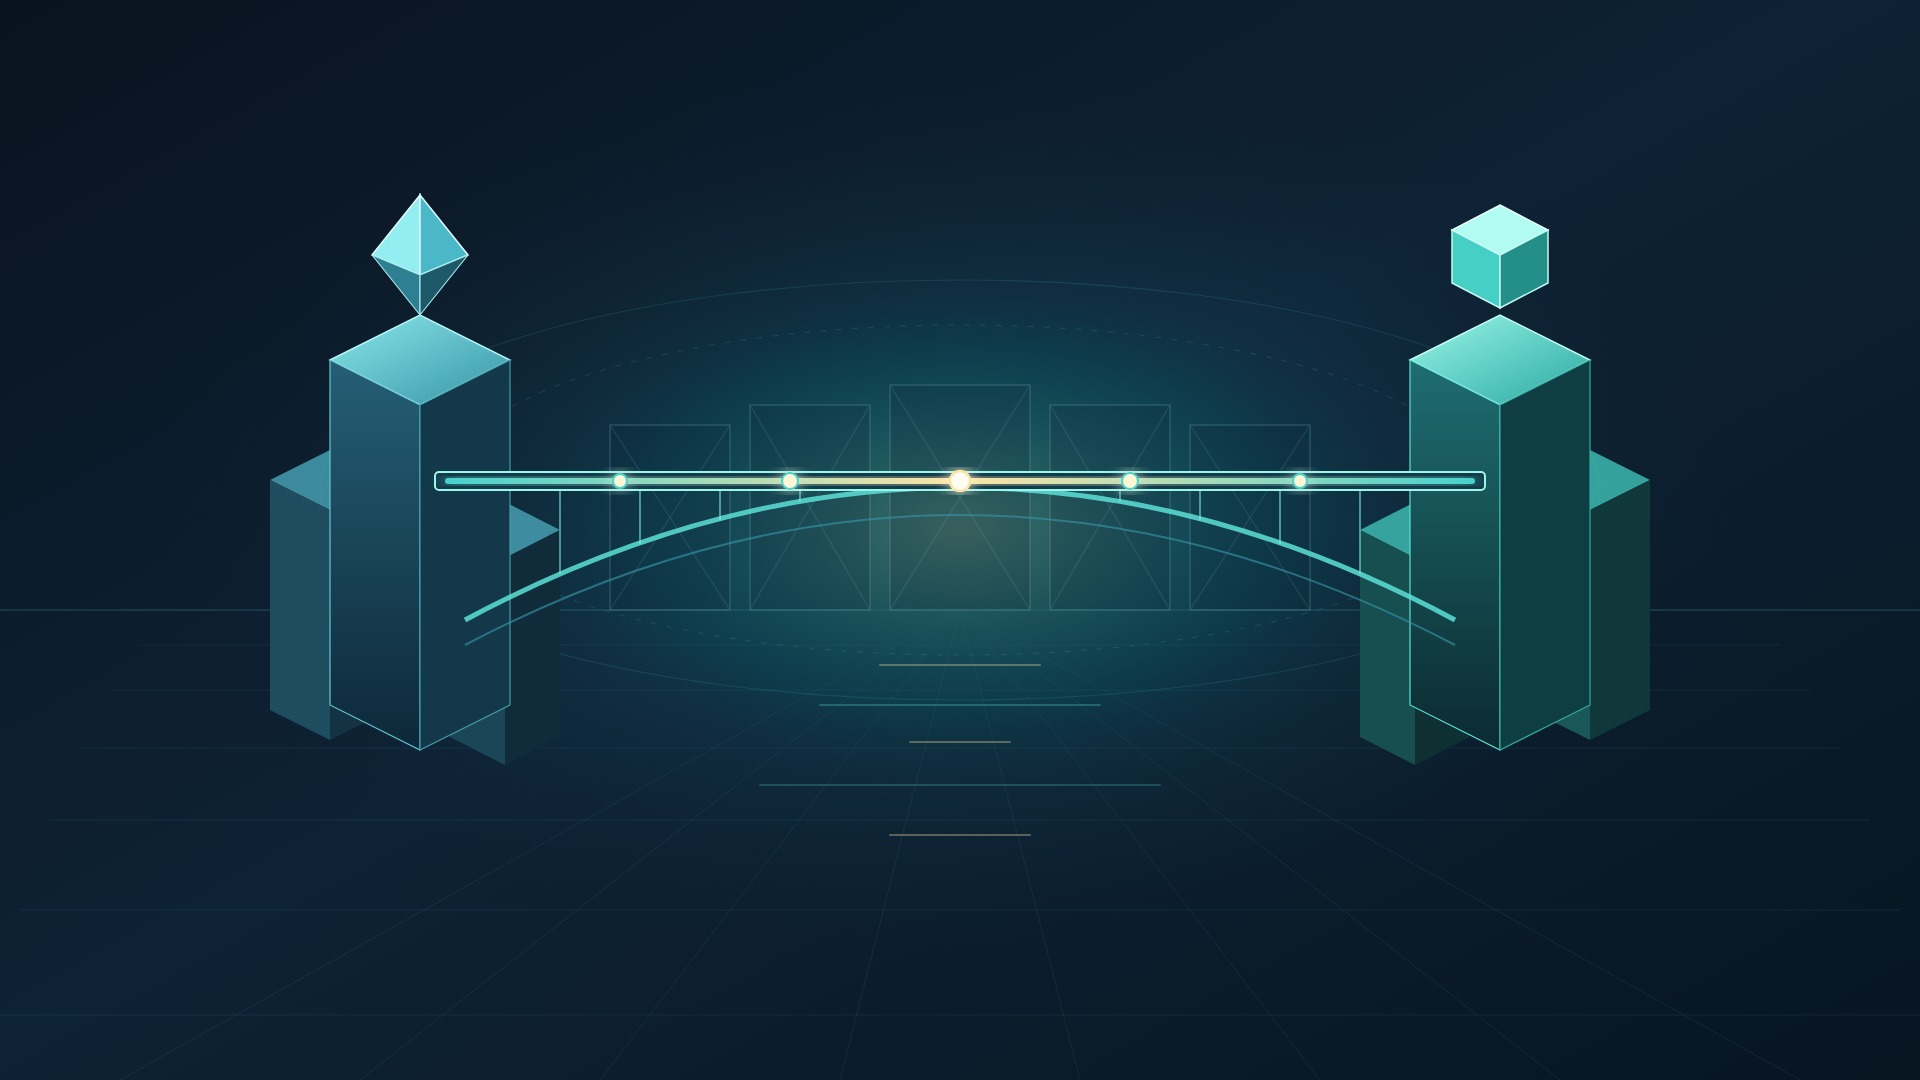
On today's internet, establishing a trusted connection between two devices or services still requires clearing three legacy hurdles: a reachable public IP, a rented DNS domain name, and an X.509 certificate from a centralized Certificate Authority. Here is how ARC (Agentic Realm Computer) and ArcBlock Chain combine in-memory self-issued DID-TLS 1.3 certificates, on-chain DID Names trust anchors, and a symmetric afs-mesh overlay to achieve Everything-over-DID connectivity, and how this architecture compares with dat://, IPFS, and Tailscale.